- Education & Events
- Advocacy
- Products & Services
- Membership
- Resources
- SDBANKER Magazine
- SDBA eNews
- SDBA eNews Archives
- Legislative Update/Bill Watch
- South Dakota Bank Directory
- Women in Banking
- Scenes of South Dakota Calendar*
- Holiday Signs
- Regulatory Report
- South Dakota Banking Code
- Record Retention Manual
- Advertising & Sponsorship Guide
- COVID-19 Resources
- Mental Health and Crisis Prevention
- About
|
News
SDBA Updates SDBA Events
Online Education
ABA Banking Journal: Audits find gaps in Fed, CFPB information security effortsOctober 29, 2026
The OIG evaluated the information security programs of the central bank and bureau as part of its annual audits. It gave both a maturity level of two out of five, meaning the programs were defined but not consistently implemented, and therefore not considered effective. Flaws included gaps in governance and datasets, outdated and incomplete policies, and a lack of coordination among IT groups. In the case of the CFPB, which has experienced significant cutbacks in staff and operations, hardware at vacated regional offices was not properly inventoried and potentially unsecured. The OIG noted the Fed and CFPB had failed to implement most of its recommendations made after its previous audits. It had eight new recommendations for both agencies on steps they should take to better secure their information systems. Back to TopABA Banking Journal: Democratic attorneys general sue FinCEN over beneficial ownership reportingOctober 28, 2026
In August, the Financial Crimes Enforcement Network, which is part of the Treasury Department, finalized a rule removing the requirement for U.S. companies and persons to report BOI to the agency under the Corporate Transparency Act. The agency also announced plans to delete previously reported information from the BOI database. In a lawsuit filed in Oregon, the attorneys general argued that the Trump administration “cannot repeal a law by rulemaking.” They asked the court to vacate the FinCEN rule, retain previously reported BOI, and order the agency to resume BOI collection. “Through the CTA, Congress required that both domestic and foreign companies report ownership information to the Treasury Department,” the lawsuit states. “Now, ignoring Congress’s judgment, the Treasury Department has promulgated a regulation that exempts from the law’s ambit all domestic companies — over 99.9% of the entities originally required to report — effectively repealing the act. Neither the Administrative Procedure Act nor the Constitution permits this lawless action." Back to TopABA Banking Journal: Fannie Mae posts updates to its AI and cybersecurity requirementsOctober 29, 2026
The revised guide changes all AI references to SI — “super intelligence” — per the Trump administration’s preference. The bulletin, however, stipulates that the updated terminology “is not intended to alter the scope, meaning, or applicability of the requirements.” Among the new requirements is a 36-hour cybersecurity incident reporting window requiring companies to provide Fannie Mae with “prompt” details about the incident, including the event date, details of actions taken and if the event caused suspension of business operations. Additional requirements were added for the development and use of SI systems, including establishing SI risk assessments, data governance standards, model training and testing controls, and monitoring SI for security risk. While Fannie Mae does not require an indemnification agreement like Freddie Mac, the updated bulletin makes companies responsible for ensuring third-party vendor compliance. The bulletin also updated the requirement that a company’s business continuity plan ensure the ability to recover from disruption of a relationship with a third-party that is “material to business conducted with Fannie Mae.” It also replaced threat assessment and continuity plan requirements with business impact analysis and added a requirement that a business continuity plan includes a communication strategy around incident response, removing a previous requirement specific to a crisis management plan. The update also removed the requirement for companies to conduct an annual threat risk assessment, as well as removed the requirement for a business continuity plan to be “formally socialized” with company leadership. It also eliminated the requirement for companies to establish contingencies for fourth-party vendors. Back to TopABA: Chair’s View: The innovation imperativeI tell my team at First Independence all the time: We have to think and act like a technology company.October 14, 2027 | Kenneth Kelly
Not long after I first arrived at First Independence Bank, I noticed a rather unique instrument sitting on a colleague’s desk at our headquarters. When I asked what it was, my staff explained to me that it was a typewriter — and that we were still using it for things like paper forms and cashier’s checks. Mind you, this was the year 2017. I told them in no uncertain terms: “You have 28 business days to get it out of here.” I share this story not as a criticism, but to illustrate how easy it can be to get stuck in legacy processes and ways of thinking. That’s why it’s essential that we build innovation into our cultures and encourage our teams to always be reevaluating what we do and how we do it. I challenge you to start with one thing today: one outdated piece of technology, one legacy process, and see what you can do to make it better. I tell my team at First Independence all the time: We have to think and act like a technology company. We’re in the business of moving money, whether it’s taking a deposit, lending or facilitating payments. We’re in the logistics of moving money. And in a competitive marketplace where consumers have many options for moving their money, we need innovation to attract and keep their business. Look at it this way: If you have to move something across the country today, are you going to reach out to the company still using a horse and buggy? Or are you going to go with the company that can offer a fast, fuel-efficient form of transportation? One of the things we did early in my tenure as CEO was to change our core system in order to better meet our customers where they are. But innovation doesn’t always have to be a multi-year, multimillion-dollar effort. Even making small process improvements, or introducing a new software product, can make teams more efficient in their day-to-day work and contribute to things like higher customer and employee satisfaction. Today, many companies are turning to artificial intelligence to enhance their business. AI can offer many benefits, but it doesn’t come without its challenges: How do we maintain the human connection that customers have repeatedly told us that they want from their bank? And how do we mitigate the risks associated with a technology that is novel and largely unregulated? These are questions banks across America are asking themselves each and every day. They’re also questions we’re asking ourselves at ABA. Our mission is to be an innovative catalyst for the nation’s banks, wherever they are in their innovation journey. When it comes to technology — especially AI — there is no “one-size-fits-all” approach to adopting and integrating these tools. Rather, each bank must deal with the technology in a way that meets them and their needs where they are. It’s a big challenge — but ABA is here to help you navigate it. In this issue of the ABA Banking Journal, you’ll find insights about how banks of all sizes are approaching innovation. You can also access ABA’s wide array of AI resources at aba.com/AI. It can be hard to know where to start with innovation. But I challenge you to start with one thing today: one outdated piece of technology, one legacy process, and see what you can do to make it better. Incremental improvements lead to large-scale growth over time — and as I like to say, if you’re not growing, you’re dying. Embracing innovation is how we ensure that our banking sector remains strong, competitive and very much alive. CISA News: CISA Unveils New Strategy to Strengthen National Cyber Defense and Critical Infrastructure SecurityOctober 26, 2026
WASHINGTON – The Cybersecurity and Infrastructure Security Agency (CISA) today released its new strategy, CISA 2030: Defend, Harden, Prevail, which advances President Trump’s Cyber Strategy for America and National Resilience Strategy while strengthening the security and resilience of the nation’s critical infrastructure. The strategy addresses an increasingly complex threat environment, strengthens national cyber defense, and prioritizes the infrastructure most essential to America’s national security, economy, public health, and safety. The threat landscape is evolving at an unprecedented pace. Nation-state actors and other malicious adversaries are becoming increasingly sophisticated in their attempts to compromise U.S. networks. CISA is strengthening national cyber defense through decisive, proactive action to identify, disrupt, and eliminate adversarial access while hardening critical infrastructure against emerging threats. “I call on every company and organization in the critical infrastructure community—from owners and operators to vendors and technology manufacturers—to act now,” said CISA Acting Director Nick Andersen. “CISA 2030 provides a focused roadmap to strengthen defenses, eliminate adversarial footholds, and deny them any advantage that could endanger the nation’s security, economy, or public health.” CISA 2030 is guided by three pillars:
The strategy also reaffirms CISA’s role, as delegated by the Department of Homeland Security, in leading the initiation and restoration of National Security and Emergency Preparedness communications, which are essential to maintaining continuity of government and public safety during crises. The strategy recognizes that cyber, physical, and geopolitical threats increasingly intersect and can disrupt essential services Americans rely on every day. CISA will work with public- and private-sector partners to strengthen the security and resilience of operational technology, advance software security, support secure emerging technologies, and improve continuity of National Security and Emergency Preparedness communications. In alignment with Cyber Strategy for America, CISA will move from a passive defense posture toward an aggressive, anticipatory stance focused on identifying, mitigating, and reducing malicious access to critical infrastructure. The agency will also improve its ability to prioritize risk, mobilize partners, and support rapid, coordinated action when threats emerge. The strategy sets out CISA’s priorities for the coming year:
CISA 2030: Defend, Harden, Prevail delivers a clear, decisive roadmap for advancing the agency’s mission and strengthening the security and resilience of the nation’s critical infrastructure in service to the American people. Back to Top |
 The Federal Reserve and the Consumer Financial Protection Bureau have both failed to make needed updates to their information security programs, which are not effective, the Fed Office of Inspector General concluded in two recent reports.
 A coalition of 21 Democratic state attorneys general has filed a lawsuit to reverse the Trump administration’s decision to scale back the scope of beneficial ownership information reporting requirements.

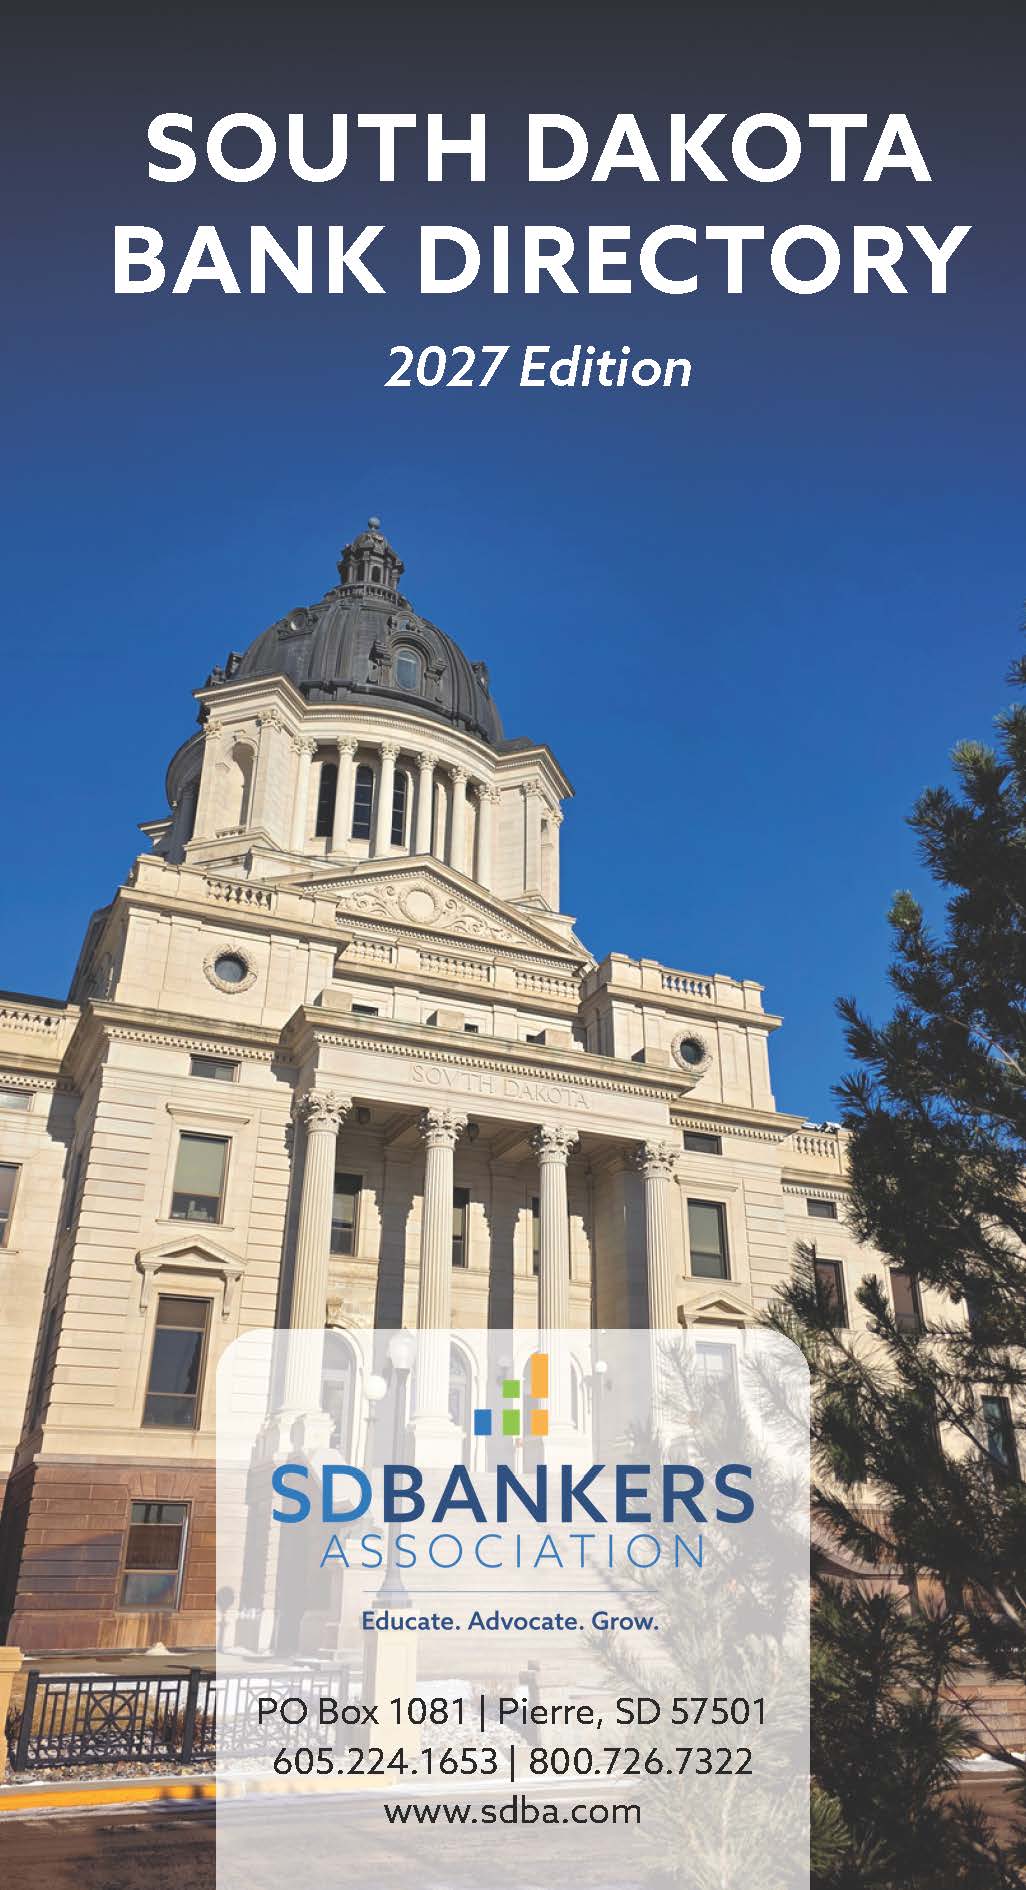 The South Dakota Bank Directory provides detailed information on all South Dakota banks including addresses, telephone numbers, important contact names and additional pertinent information. The directory also contains information on the SDBA, banking associations, regulatory agencies, endorsed vendors, associate members and South Dakota officials.